Engineering Software Lab (ESL) | Case file SRP-DRILL-2026-09-14CoverExhibits24h72hFinal
ESL SBOMator 1.4.7
Software supply-chain evidence for the Cyber Resilience Act
Software supply-chain evidence for the Cyber Resilience Act
From product scan to ENISA report,
in nine moves
CRA Article 14 reporting obligations apply since 11 September 2026. This file walks through how ESL SBOMator finds the risk, verifies it, and prepares the Early Warning, the 72-hour Notification and the Final Report for the ENISA Single Reporting Platform. Every exhibit is a real 1.4.7 screen; every teleprinter line is real tool output from a labelled drill.
Drill: nothing filed with ENISAReal screenshotsReal tool output
← swipe or use the arrow keys →
Exhibit A | Main window, Project Scan, captured 2026-09-13CoverExhibits24h72hFinal
MOVE01
Scan the product once; get SBOM, VEX and HTML report
A
B
C
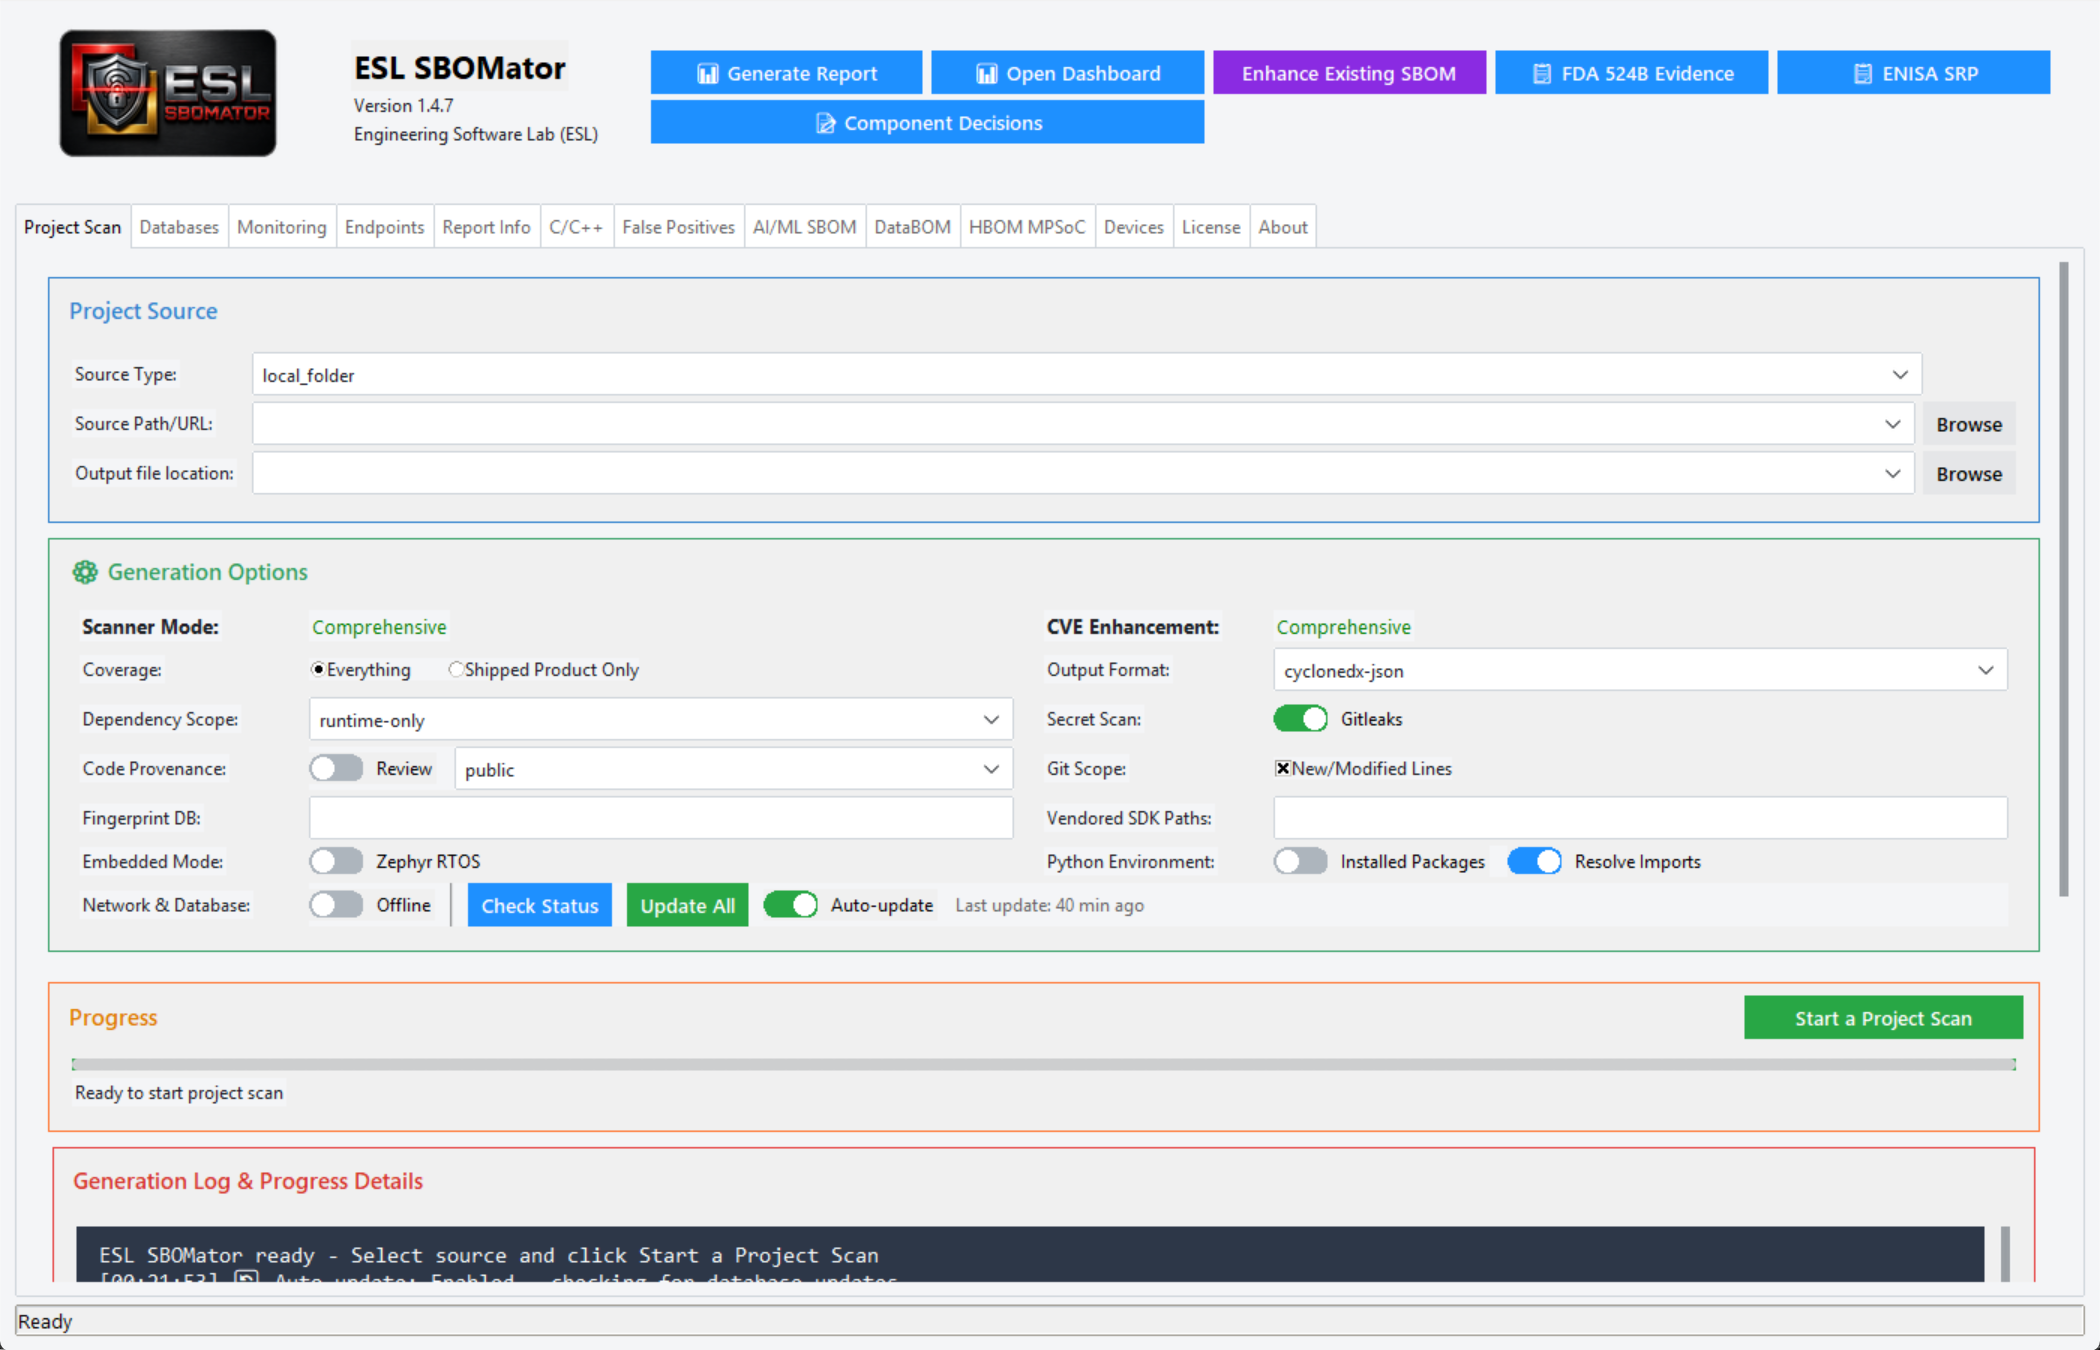
Exhibit A. ESL SBOMator 1.4.7, Windows, 1400x900 at 150% DPI.
A
Start a Project ScanOne click runs the parsers, matches CVEs against NVD, OSV, KEV and EPSS, and writes CycloneDX 1.6 SBOM, VEX and an HTML report.
B
ENISA SRPThe CRA reporting workspace is one click from the header, next to FDA 524B evidence.
C
13 workspaces, no clipped titlesProject Scan, Databases, Monitoring, Endpoints, C/C++, AI/ML SBOM, DataBOM, HBOM MPSoC, Devices and more. ENISA SRP opens as a 14th.
Exhibit B | Dashboard, ArduPilot scan, 157 componentsCoverExhibits24h72hFinal
MOVE02
Read the whole risk picture on one page
1
2
3
4
5
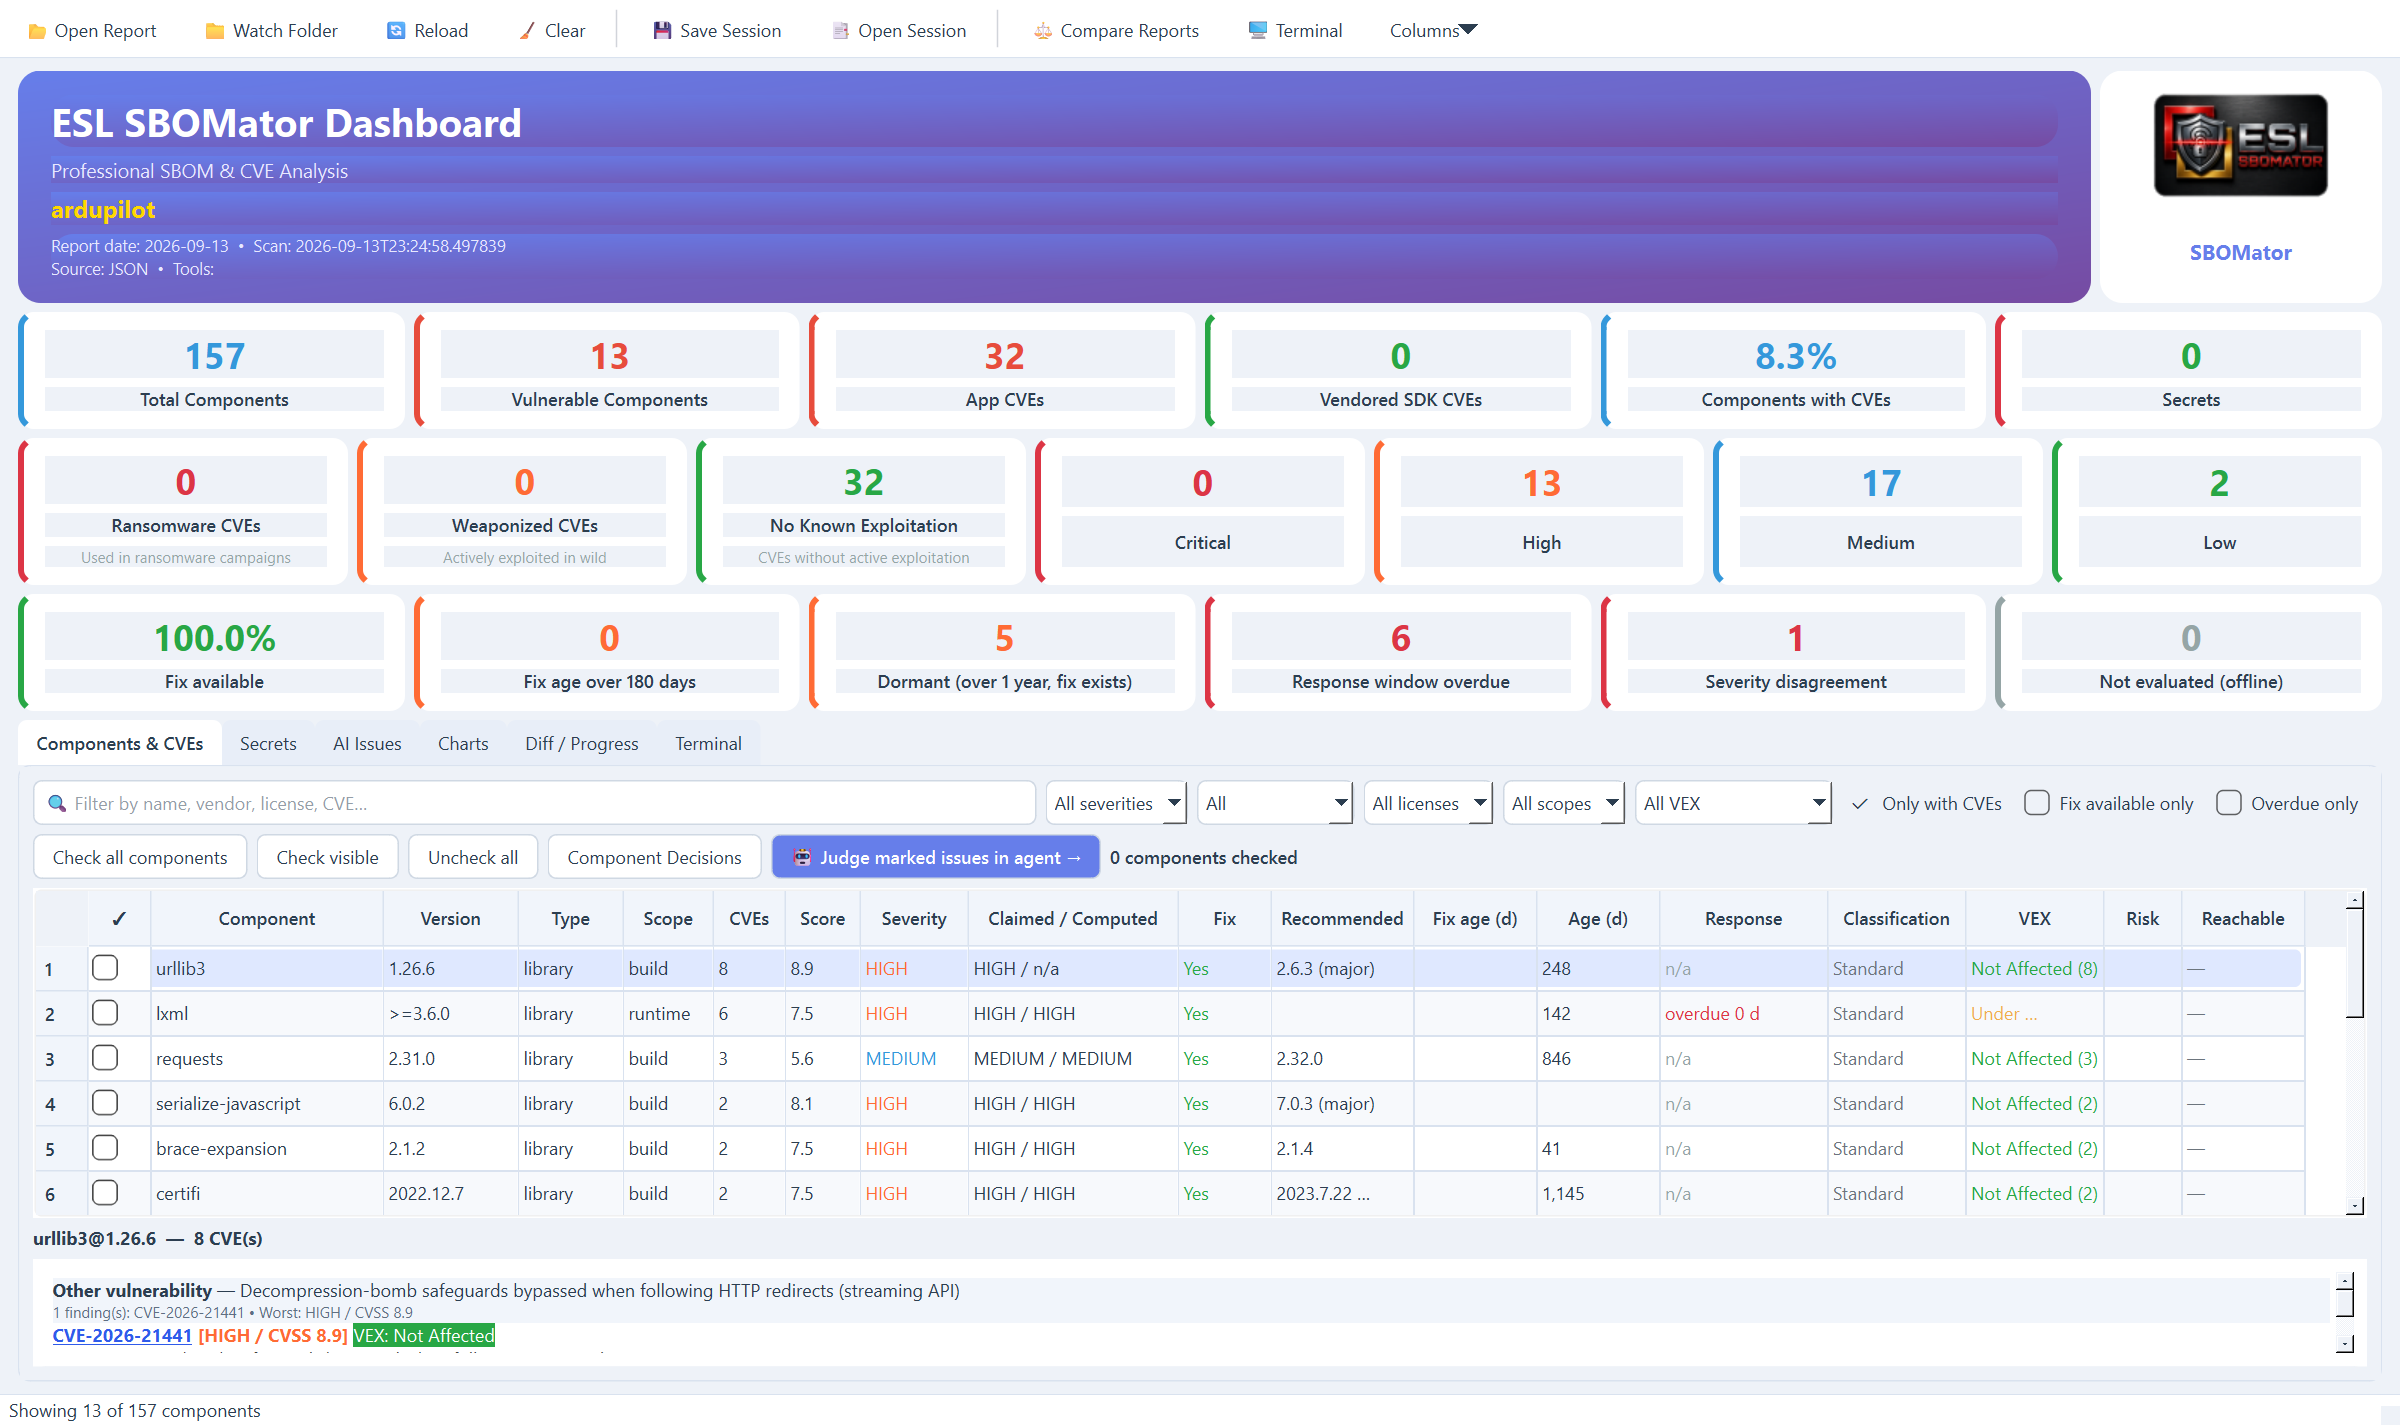
Exhibit B. PySide6 dashboard, ArduPilot at commit 37ea692, scan 2026-09-13.
1
157 components, ArduPilotOpen-source flight controller used as the frozen acceptance baseline.
2
32 CVEs, 13 High, 0 CriticalClaimed severity beside computed severity; disagreements are counted, not hidden.
3
100% fix availableEvery finding has a recommended version. Unknowns are excluded from the denominator, never counted as fixed.
4
6 response windows overdueFix published, window passed, still unpatched. The first question a regulator asks.
5
5 dormant findingsFix has existed for over a year. Reachability decides whether they become policy violations.
Exhibit C | AI Issues, CI/CD reference verificationCoverExhibits24h72hFinal
MOVE03
Verify the build pipeline itself: 14 CI/CD actions, 14 unpinned
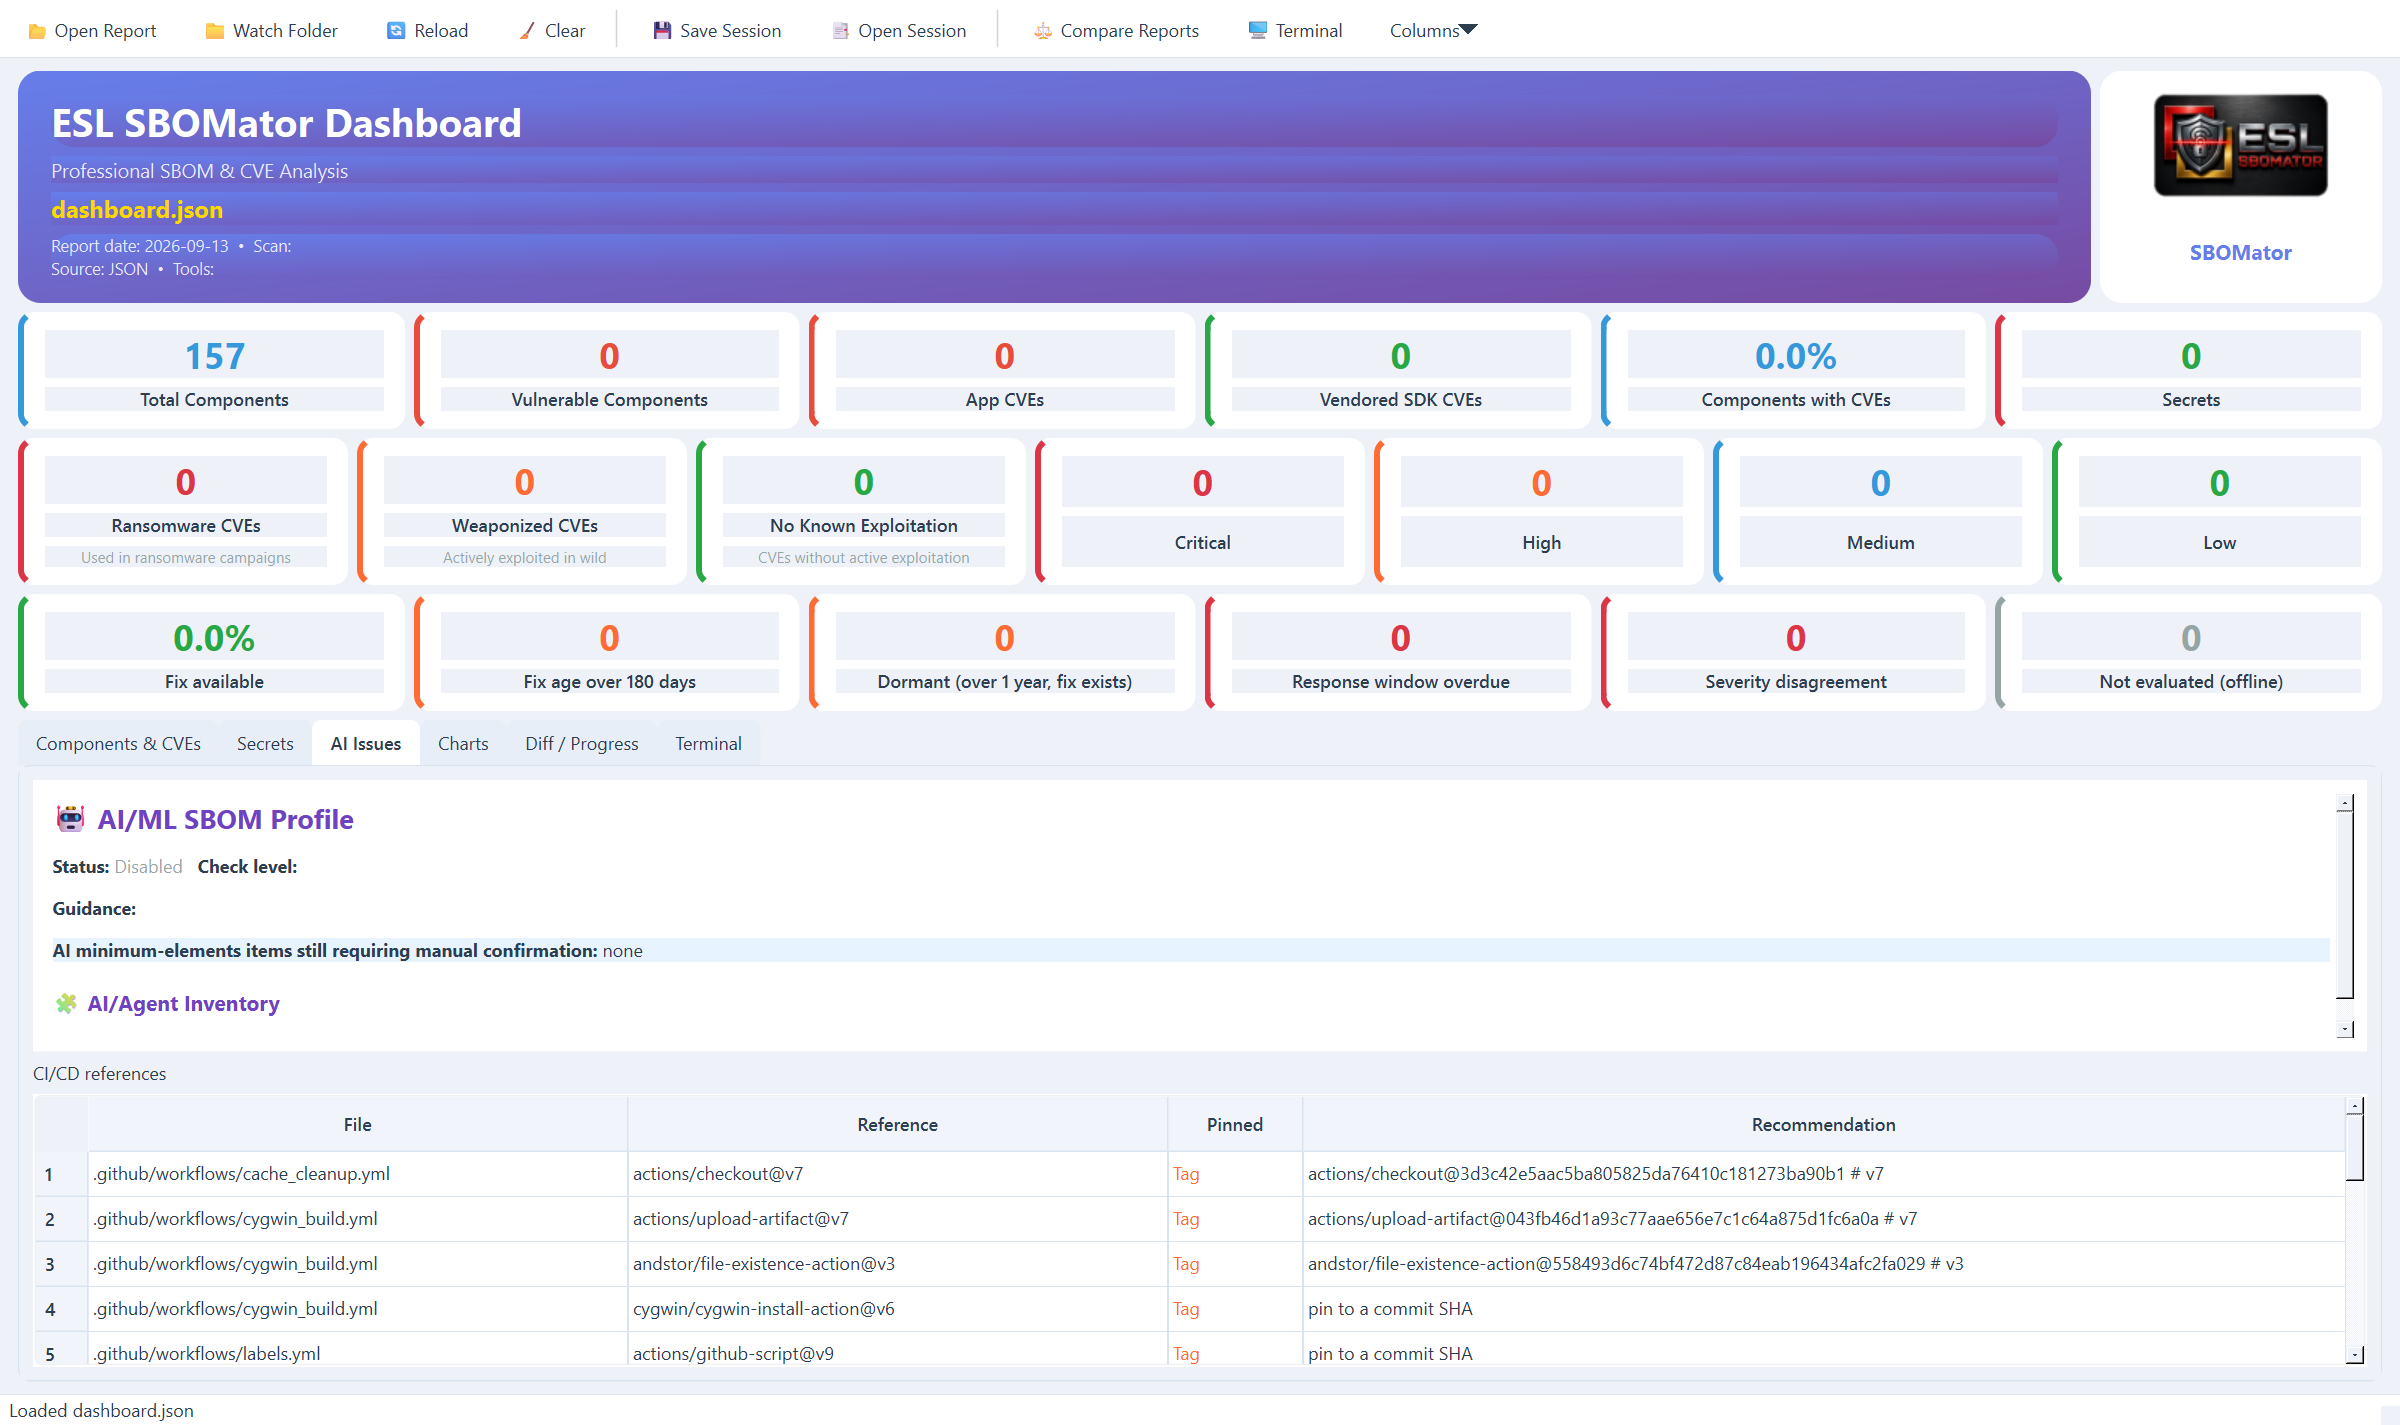
Exhibit C. GitHub Actions and pre-commit hooks from 32 ArduPilot workflow files.
1
Every
uses: line becomes a pkg:github componentThe pipeline is inventoried in the SBOM, not only the application dependencies.2
Nonexistent owners are flaggedHallucinated or squatted names such as
acme-nonexistent-owner/setup-thing are caught before they run in CI.3
Tag pins get a SHA recommendation
actions/checkout@v6 becomes a full 40-character commit pin, ready to paste.4
The policy gate can fail the buildEnable
fail_on_unpinned_actions and the CLI exits 2 with a machine-readable violation list.Teleprinter T-5 and Exhibit D | submission logCoverExhibits24h72hFinal
MOVE09
Log the portal submission: the clock clears, the case moves to 72h
Logged== 8. Simulate the human portal submission (no real portal contact)
Submission log entry: {"stage": "24h", "who": "drill-operator",
"submitted_at": "2026-09-14T05:42:28Z", "portal_reference": "DRILL-EW-000001"}
Stage after submission: 72h
Clock text after submission: ''
== 9. Integrity checks
audit chain valid: True
snapshots valid: True
72h validation errors now: none
D
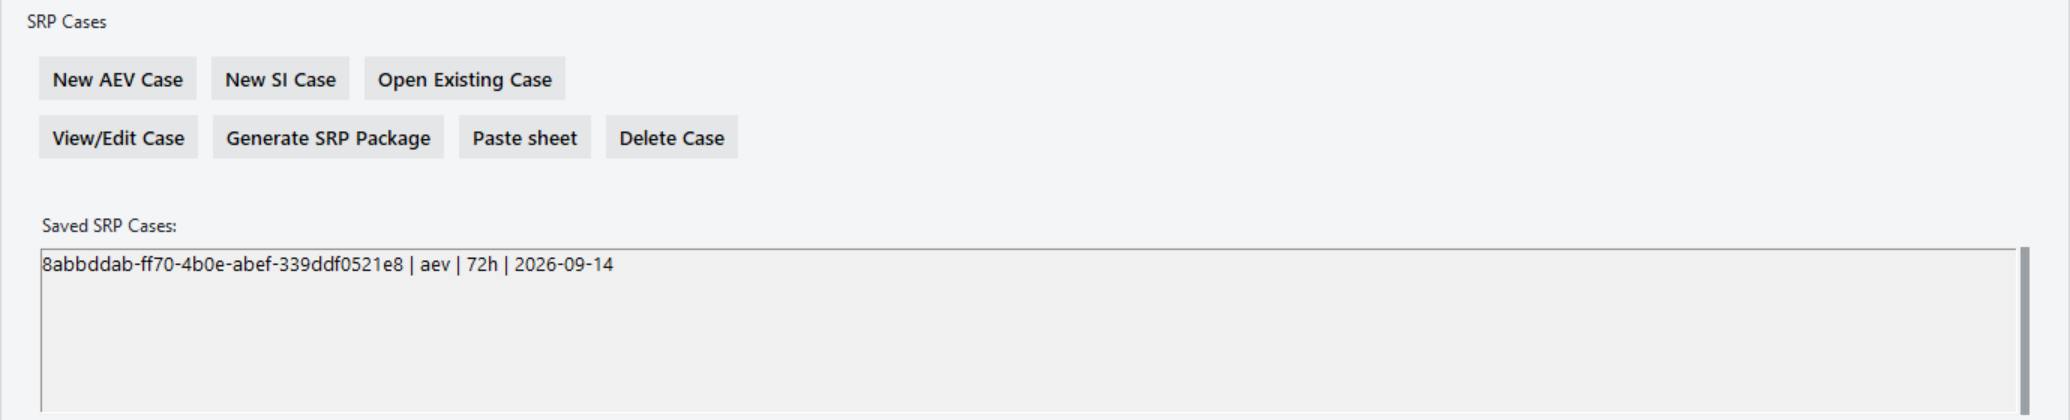
Exhibit D. ENISA SRP tab, Saved SRP Cases.
D
Saved SRP Cases: aev | 72hThe GUI lists the same case, now at the 72-hour Notification stage. Delete Case removes the drill when the exercise ends.
Case file SRP-DRILL-2026-09-14 | closedCoverExhibits24h72hFinal
Engineering Software Lab (ESL)
Nine moves. One evidence trail.
Ready for 11 September 2026.
ESL SBOMator 1.4.7: CycloneDX 1.6 and 1.7 SBOM and VEX, readiness counters, CI/CD reference verification, a policy gate for CI, and the ENISA SRP case workflow with paste sheet, package manifest and audit chain.
Windows, Linux, macOSGUI, dashboard, CLIOffline capableCase closed
Related: ESL Solutions for CRA | Real-time supply-chain threat detection | Hallusquatting protection